Compliance, Risk & Fiscal
Protect the whole company.
Tax, data protection (LGPD), risk, whistleblowing, contracts and AI governance in one product. A work-accident report from People and a sanctions hit from Treasury become risks here.
- 17 modules
- 2 products send it events

What Compliance does
Fiscal & Tax · Fiscal Documents
Every invoice in a single register.
The company’s NF-e, NFS-e and CT-e, Brazil’s electronic invoices for goods, services and freight, each with its access key, type, status and amount. Rejected ones stay in plain sight.
Authorization at SEFAZ, the state tax authority, uses your company’s ICP-Brasil digital certificate and is switched on at implementation.

Grupo Vértice’s invoices with key and status; the notice at the top lists the credentials implementation connects.Grupo Vértice · fictional company · illustrative data Fiscal & Tax · Tax
Every tax with a date and an amount.
Each group company’s tax calendar follows from its own regime: federal payments and returns (DARF for PIS and COFINS, DCTFWeb, EFD-Reinf), the DAS of Simples Nacional companies, the municipal ISS and the ECD and ECF digital ledgers, each with its due date, status and amount.

Grupo Vértice’s tax calendar, obligation by obligation.Grupo Vértice · fictional company · illustrative data GRC Suite · LGPD Workbench
The LGPD, with the clock running.
Data subjects file requests through your company’s Privacy Center and get a code to follow them. The 15-day deadline runs on its own; an incident brings the 3-business-day deadline to notify the ANPD, Brazil’s data-protection authority.

Grupo Vértice’s data-subject requests, each with its own deadline.Grupo Vértice · fictional company · illustrative data GRC Suite · ERM
Risk on a map, not a spreadsheet.
Every risk with inherent, residual and target scores on the likelihood-and-impact map, with indicators and a board report. A work-accident report (CAT) from People and a sanctions hit from Treasury come in with no retyping.
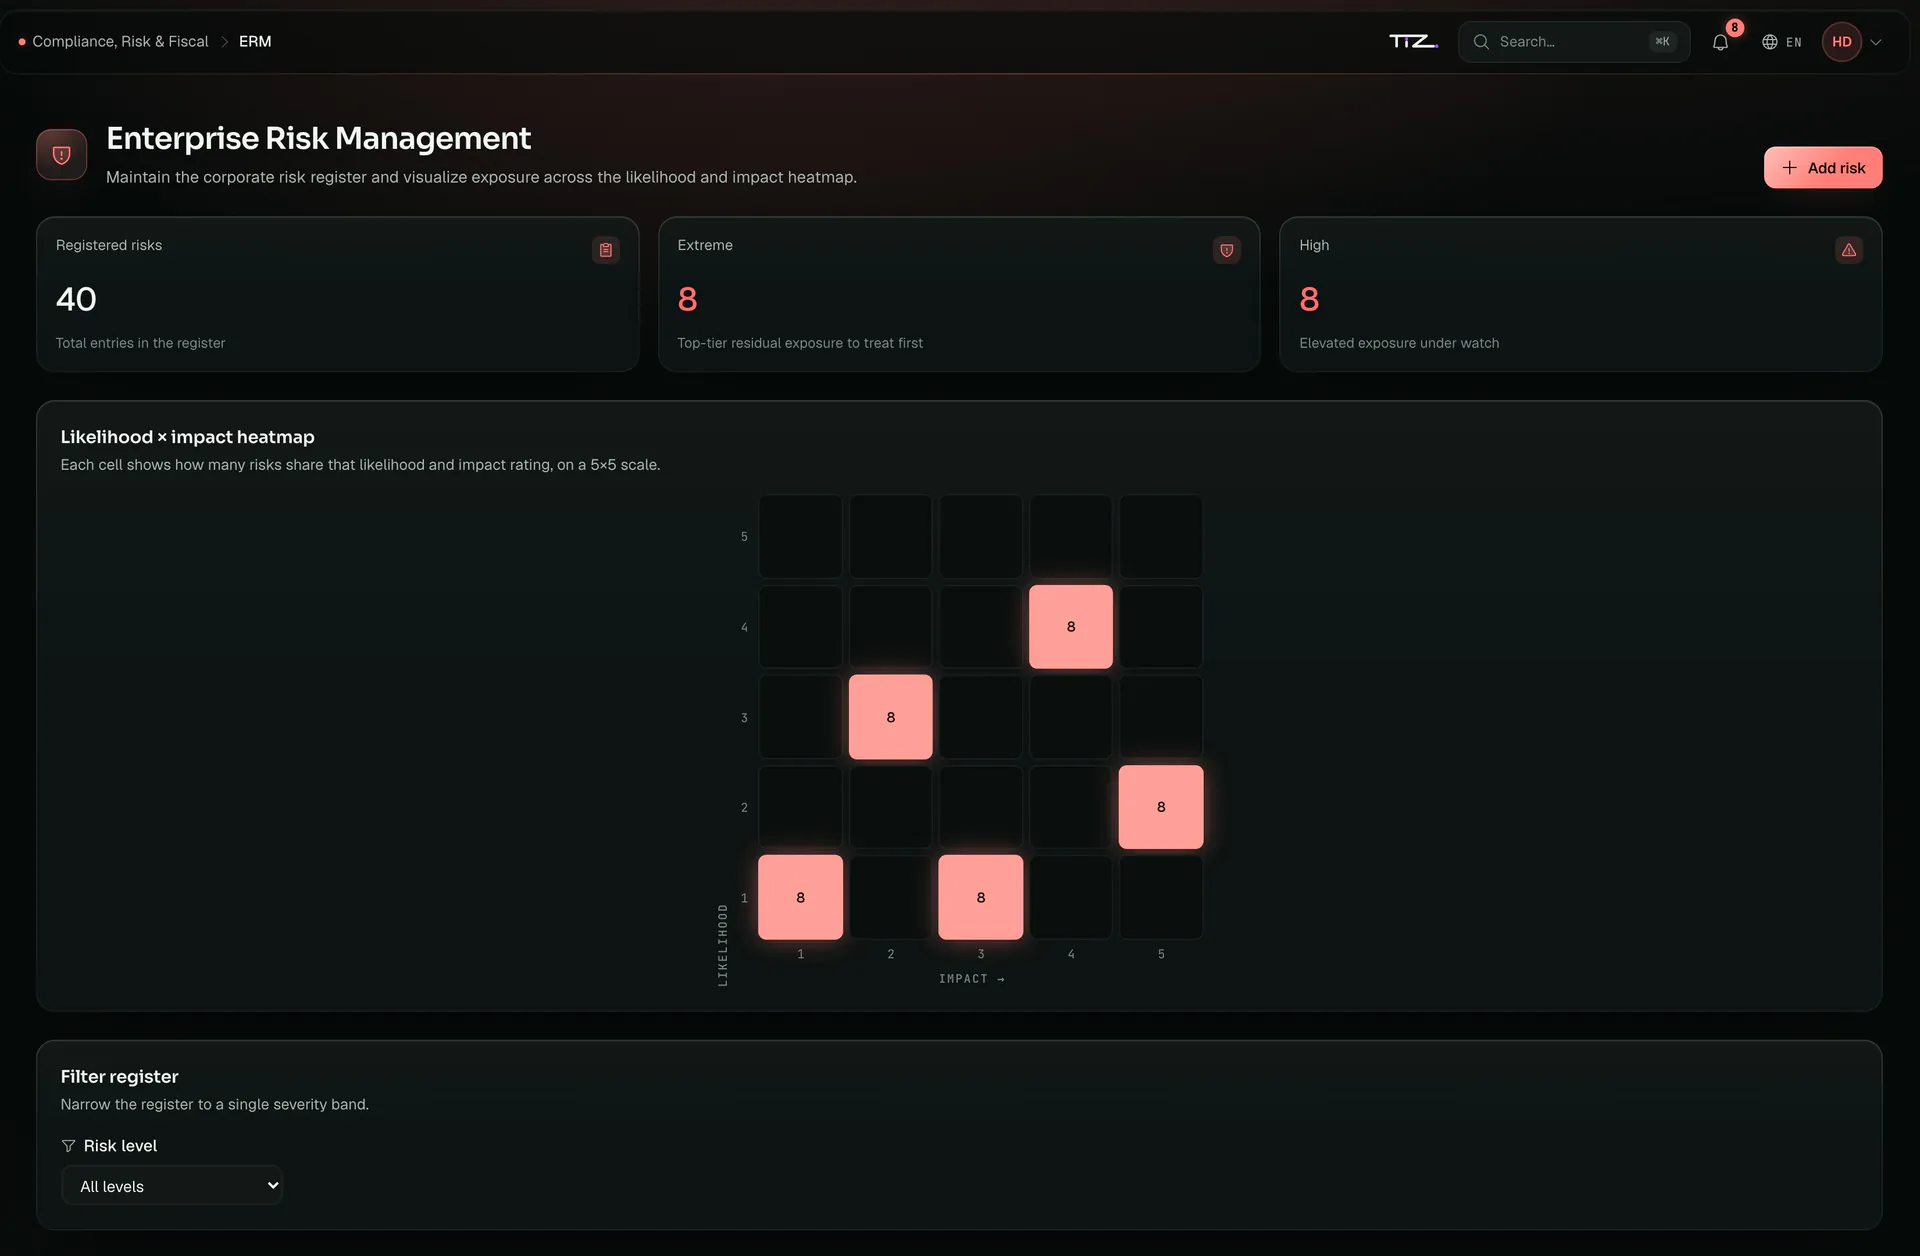
Grupo Vértice’s risks on the likelihood-and-impact map.Grupo Vértice · fictional company · illustrative data
17 modules, as the product shows them.
The same groups and the same names as the Compliance menu.
Tax and LGPD, deadline by deadline.
Brazil’s rules are already in the product: fiscal documents, obligations by regime, LGPD deadlines and the whistleblowing channel the law requires.
Marked items are switched on at implementation, with your company’s certificates and credentials.
NF-e, NFS-e and CT-e
In a single register, with each document’s access key and status. SEFAZ authorization uses your company’s ICP-Brasil certificate.
SEFAZ and contingency
The authorizers of all 27 UFs, every state plus the Federal District, are in the tax engine. Contingency through SVC-AN and SVC-RS, by state.
Obligations by regime
Simples Nacional for small businesses, Lucro Presumido (presumed profit), Lucro Real (actual profit) or MEI for sole traders: each company’s tax regime decides which of DCTFWeb, EFD-Reinf, DAS, ECD and ECF enter its calendar.
LGPD deadlines
15 days to answer the data subject and 3 business days to report an incident to the ANPD, counted by the system.
Whistleblowing channel
The deadlines of Lei 14.457/2022 and the reporter’s anonymity: an identity is revealed only with the CISO, DPO and Legal together.
Clean Company Act
The integrity program under Lei 12.846/2013, scored against the CGU matrix and the Decreto 11.129/2022 checklist.
Talks with 2 products.
The real events that arrive from the other products, and what each one changes in Compliance.
Only events that already take effect in the receiving product appear here. CPF, CNPJ, phone, Pix key and address stay out of events between products.
How the products talkCommon questions
Do I need other products to use Compliance?
No. Compliance works on its own, and TIZ comes included. With People or Treasury active, a filed CAT and a counterparty on a sanctions list arrive as risks in ERM.
Does Compliance authorize NF-e at SEFAZ?
Authorization uses your company’s ICP-Brasil certificate and is switched on at implementation, with contingency through SVC-AN and SVC-RS. NF-e, NFS-e and CT-e are gathered in Compliance, each with its access key and status.
How does Compliance handle LGPD requests?
Data subjects file requests through your company’s public Privacy Center and get a code to follow them. The 15-day deadline runs from the request, and each incident brings the 3-business-day deadline to notify the ANPD.
How does the whistleblowing channel protect the reporter?
The channel opens through a public link, with no login. Reporters get a code to follow the case and reply without identifying themselves; if there is an identity, it is revealed only with the CISO, DPO and Legal together.
How does Compliance govern the company’s AI?
Every AI use goes through your company’s policy: enablement per capability, a monthly cost cap and automatic shutdown if accuracy drops. AI agents query controls and evidence through the MCP server, with role-based permission.
Where is Compliance data stored?
In São Paulo, with each company isolated from the others by the database itself. The digital certificate is kept in a vault, never in the database.